
Fake Zoom Installers Put macOS Users at Risk From CloudSyncD Backdoor
macOS has long benefited from a strong reputation for built in security protections. However, attackers continue to find ways around those protections by targeting the human element. A newly identified malware campaign demonstrates this approach through a fake Zoom installer carrying a backdoor known as CloudSyncD. According to research from Jamf Threat Labs, the malware […]
Microsoft X Account Hijack Highlights the Growing Risk of Social Media Account Takeovers
A trusted corporate social media account can become a powerful tool for cybercriminals when compromised. Microsoft recently confirmed that its official X account was taken over and used to promote a cryptocurrency related campaign. The account has more than 13 million followers, giving attackers access to a large and highly trusted audience. The incident demonstrates […]
Windows 11 Makes Enterprise Backup a Default: What Security Teams Need to Know
Microsoft is changing the way organizations approach Windows device resilience. With the release of Windows 11 version 26H2, Windows settings backup and restore, formerly known as Windows Backup for Organizations, is now enabled by default for eligible enterprise devices when administrators have not explicitly configured the backup policy. Existing administrator settings, whether enabled or disabled, […]
Armadin Raises $255 Million as AI-Powered Cybersecurity Moves Toward Autonomous Attack Simulation
Artificial intelligence is changing how organizations approach cybersecurity. The latest development comes from Armadin, the AI-native cybersecurity company founded by Kevin Mandia, which has raised approximately $255.5 million in a new funding round. The Series B investment brings Armadin’s total funding to approximately $445 million and places the company’s reported valuation above $2.5 billion. The […]
AI Agents Are Moving Into the Real World: Why Agentic AI Needs Security, Governance and Accountability
Artificial intelligence is moving from systems that respond to instructions toward autonomous agents capable of planning tasks, using tools, accessing systems, and operating for extended periods with limited human supervision. That shift creates significant opportunities for organizations, but it also introduces a new cybersecurity and governance challenge. Recent developments involving Anthropic and OpenAI are bringing […]
ShinyHunters Under Pressure: What the FBI Arrest and Extortion Campaigns Mean for Enterprise…
The cybercrime group ShinyHunters is facing increased pressure from international law enforcement following the arrest of a suspected member in the Netherlands and a public appeal from the FBI for remaining members to come forward. The development comes after a series of high profile data theft and extortion campaigns targeting organizations across multiple industries. The […]
Apple Patches Actively Exploited Zero Day: A Warning for Enterprise Mobile Security
Apple has released security updates addressing a zero day vulnerability that was reportedly exploited in targeted attacks against specific individuals. The vulnerability, tracked as CVE-2026-20700, affects dyld, Apple’s Dynamic Link Editor, a core component responsible for loading dynamic libraries used by applications and system frameworks. Apple disclosed that the vulnerability may have been exploited in […]
NeedyMantis Malware: How Attackers Are Turning Trusted Software Into a Path to Long Term Access
Modern cyberattacks are increasingly designed to remain hidden after an attacker has already gained access to an organization. A recent analysis by Microsoft Threat Intelligence of a malware family called NeedyMantis highlights this evolving threat. The malware has been observed in targeted intrusions involving telecommunications organizations, universities, medical nonprofits, intergovernmental organizations, and government contractors. The […]
PHP URL Validation Flaw Highlights the Risk of Credential Exposure
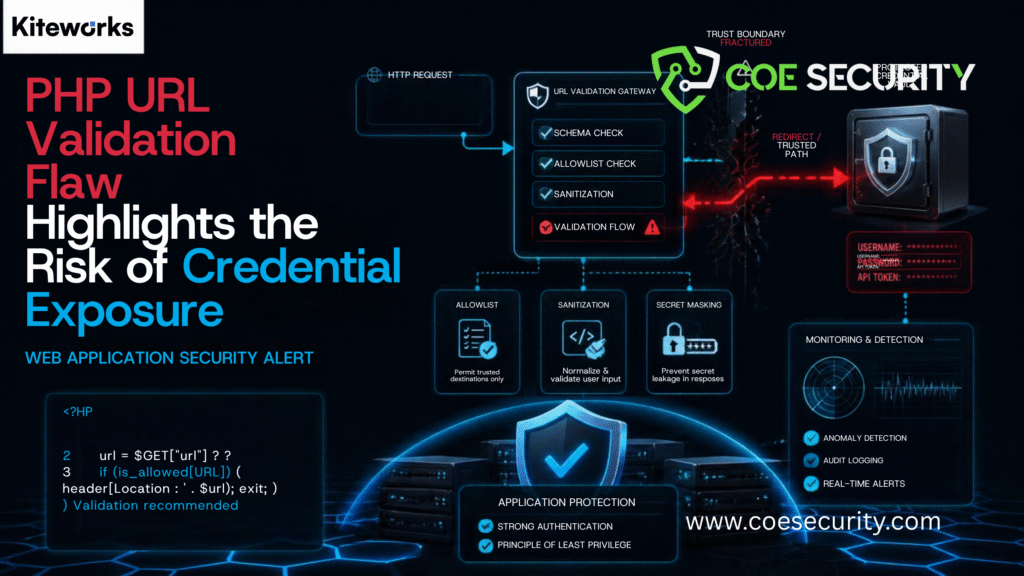
A vulnerability in PHP’s URL validation functionality has highlighted an important application security lesson: input validation errors can sometimes create security consequences far beyond an application’s expected behavior. The issue, tracked as CVE-2021-21705, affected PHP versions in which FILTER_VALIDATE_URL could incorrectly validate specially crafted URLs. PHP classified the issue as an SSRF bypass, and the […]
Kiteworks Vulnerability Highlights the Importance of Rapid Response to Emerging Threats
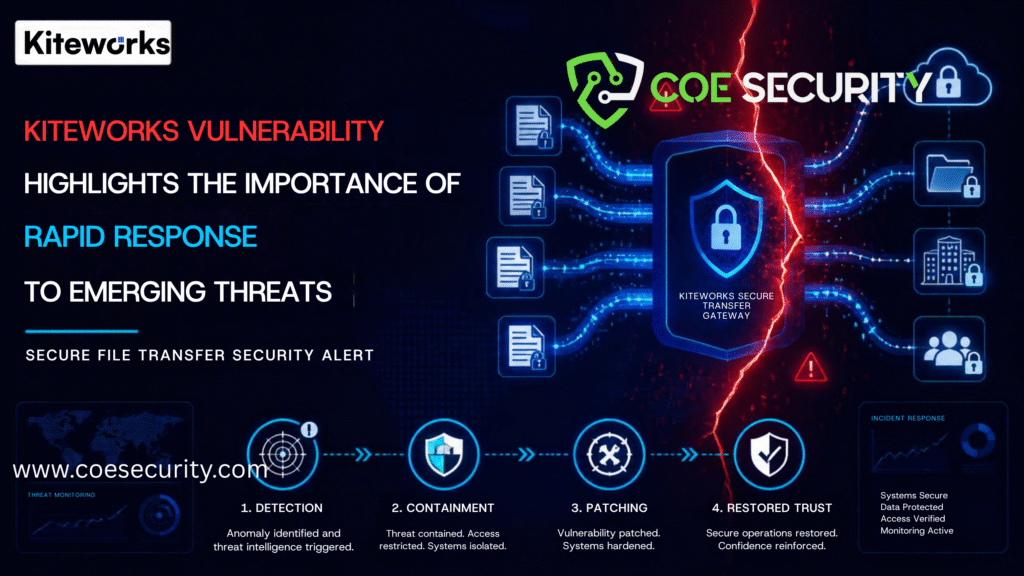
Cybersecurity incidents do not always begin with a confirmed breach. Sometimes, credible intelligence about a potential threat is enough to require immediate defensive action. A recent security incident involving Kiteworks, a secure data sharing and collection platform, highlights this challenge. The company temporarily advised customers to shut down certain self hosted and on premises systems […]