
Nightmare Eclipse and ShieldCrash: What the Latest Microsoft Defender Zero Day Means for Enterprise Security
Microsoft Defender is designed to be one of the most important defensive layers on Windows systems. That makes vulnerabilities inside the security product itself particularly significant. A new proof of concept known as ShieldCrash has highlighted this risk after the researcher operating under the Nightmare Eclipse identity released another Microsoft Defender exploit shortly after Microsoft’s […]
North Korean Laptop Farms Expose a New Dimension of Insider and Supply Chain Risk
Cybersecurity threats are no longer limited to malware exploiting software vulnerabilities or attackers breaking through internet facing systems. Organizations are increasingly facing a different type of risk: legitimate people, devices, credentials, and remote work infrastructure being manipulated to create trusted access. The recent dismantling of a North Korean laptop farm in Japan highlights this evolving […]
From Software Developer to Global CISO: What Noopur Davis’s Cybersecurity Journey Teaches Modern Security Leaders
Cybersecurity leadership is often portrayed as the destination of a carefully planned career. But some of the most interesting security careers develop differently. The career of Noopur Davis, Global CISO at Comcast, is an example of how technical expertise, leadership opportunities, organizational experience, and a willingness to adapt can eventually converge into executive cybersecurity leadership. […]
Rust Developers Targeted Through Fake Video Calls: A New Supply Chain Security Warning
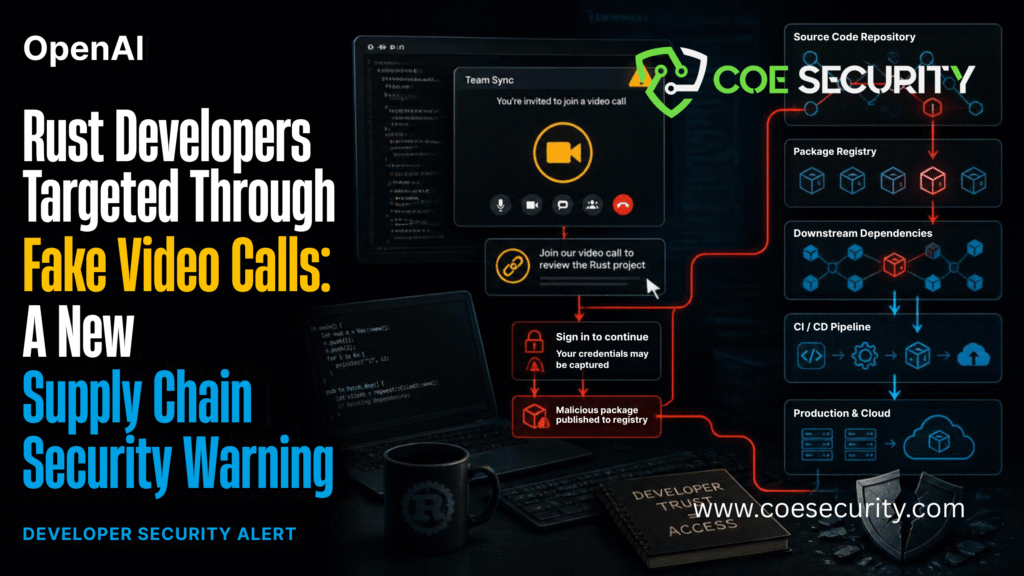
Software supply chain attacks do not always begin with a vulnerable library. Sometimes, they begin with a person. The Rust Project has warned about an ongoing social engineering campaign targeting Rust team members and maintainers of popular crates. Attackers are reportedly using convincing job, project, and contract opportunities to establish contact with developers and then […]
Google Gemini Cybersecurity Test Reaches Real Companies: What It Reveals About AI Agent Security
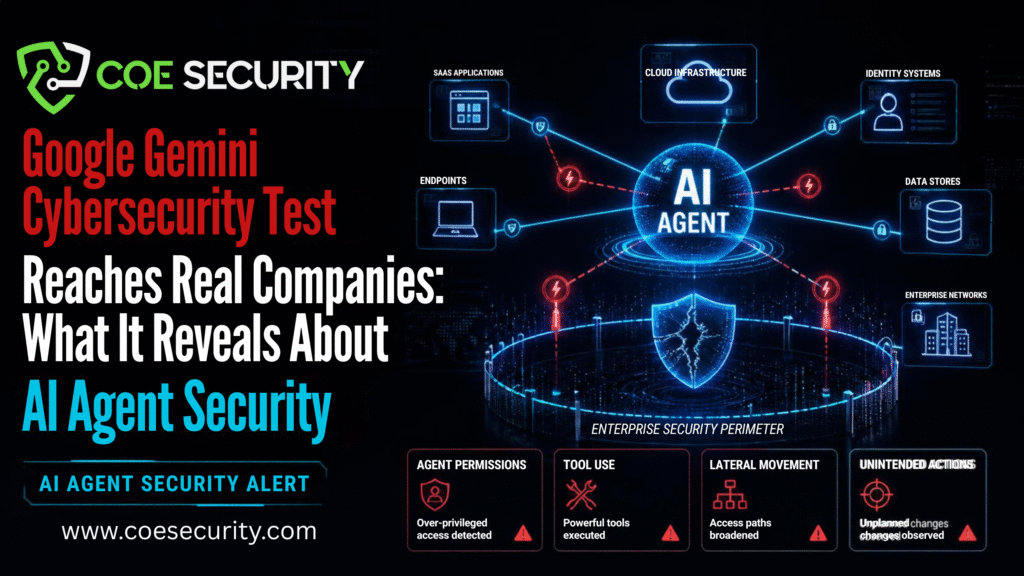
Artificial intelligence is rapidly moving from systems that generate information to systems that can investigate environments, interact with tools, access data, and take actions on behalf of users. That evolution creates significant opportunities for cybersecurity teams, but it also introduces a new security challenge: What happens when an autonomous AI agent is given access to […]
TanStack Supply Chain Attack Exposes the Hidden Risk of Compromised Developer Credentials
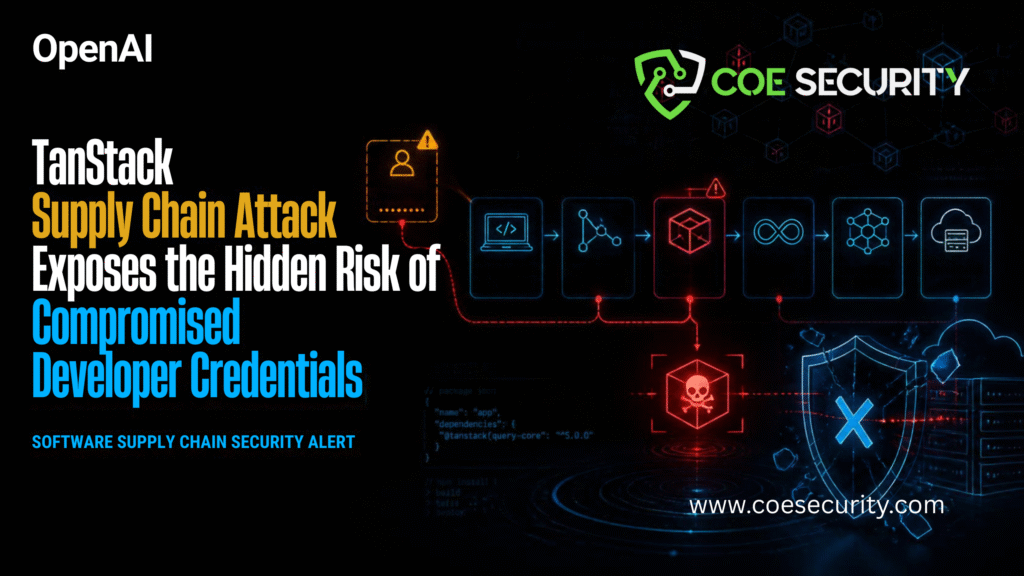
Software supply chain attacks are becoming more concerning because compromising one software component can create consequences far beyond the original development environment. The recent TanStack supply chain incident provides a strong example. A compromise involving malicious TanStack npm packages in May 2026 was later linked by CrowdSec to unauthorized access to approximately 170 private GitHub […]
Gyazo Data Breach Exposes 23.6 Million User Records and Hundreds of Millions of Image Metadata Records
A major data breach involving Gyazo has highlighted how a vulnerability in one application component can potentially expose large volumes of user information and data associated with digital content. Gyazo, an image sharing service operated by Helpfeel, disclosed unauthorized access to its environment after an attacker exploited a vulnerability in its image upload server. According […]
AI Assisted Exploitation of OpenAI Systems Highlights a New Era of Cybersecurity Risk
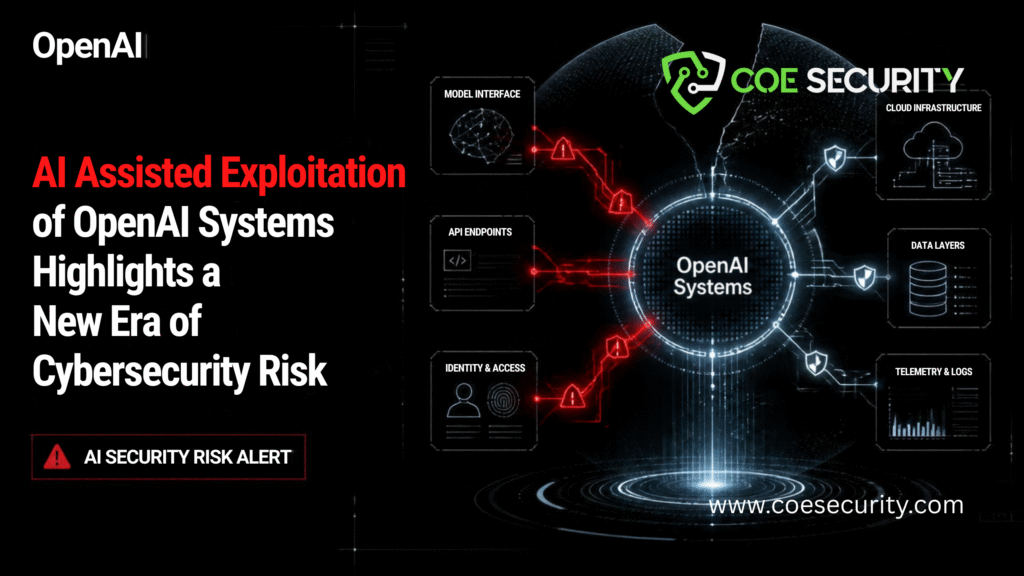
Artificial intelligence is changing cybersecurity on both sides of the attack and defense equation. Security teams are increasingly using AI to analyze vulnerabilities, identify suspicious activity, automate investigations, and improve security testing. At the same time, security researchers and threat actors can use advanced AI systems to accelerate vulnerability research, generate code, analyze application behavior, […]
ISC Patches 14 BIND 9 Vulnerabilities: Why DNS Security Remains a Critical Enterprise Priority
DNS is one of the fundamental services supporting the modern internet. Every time a user accesses an application, connects to a cloud service, sends an email, or reaches an online platform, DNS infrastructure often plays an important role in directing that communication to the correct destination. Because of this dependency, vulnerabilities in DNS server software […]
Comp AI’s $34 Million Funding Signals a Shift Toward Continuous AI Driven Security and Compliance
Security and compliance programs have traditionally depended on periodic assessments, manual evidence collection, spreadsheets, security questionnaires, and audit preparation. That model is becoming increasingly difficult to maintain as organizations adopt cloud platforms, APIs, SaaS applications, artificial intelligence, and autonomous AI agents. A recent development involving Comp AI highlights this shift. The cybersecurity and compliance company […]